
| Title | IT Auditor |
|---|---|
| Department | Internal Audit / IT Audit / Assurance |
| Reports to | [IT Audit Manager / Director of Internal Audit / Chief Audit Executive] |
| Location | [Remote / Hybrid / On-site] |
| Employment type | Full-time |
| Experience | [3 to 6] years |
| Salary | [Pay range, currency and pay period, plus any bonus and material benefits. Check the pay-disclosure rules for each location where you post.] |
Position overview
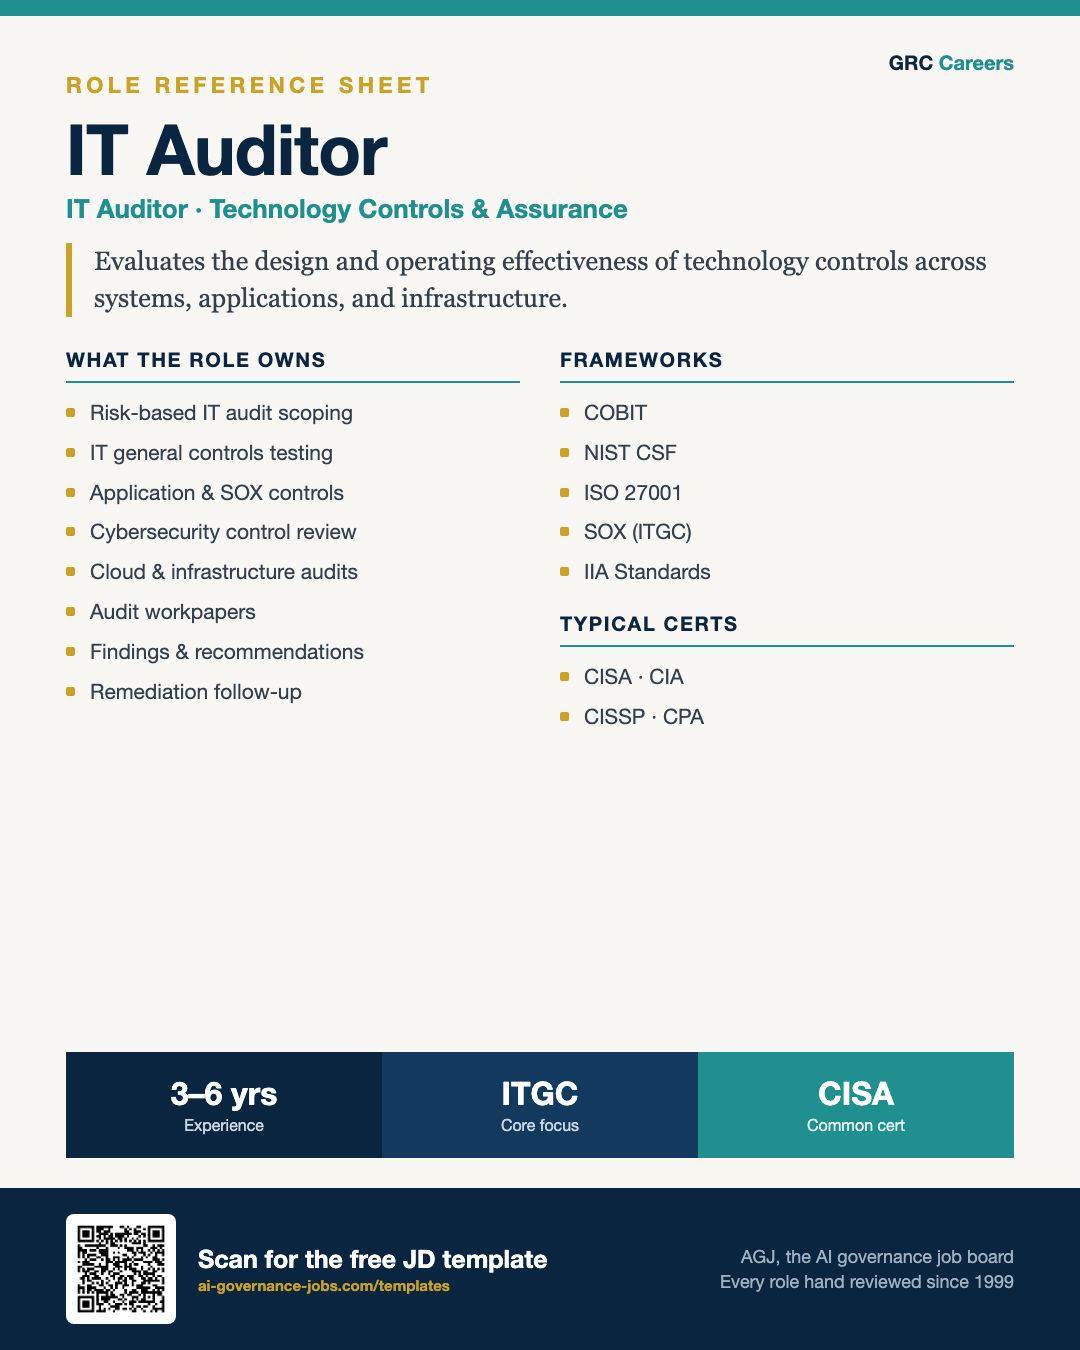
The IT Auditor plans and executes audits of [Company]'s technology environment, assessing whether IT controls are well designed and operating effectively. This includes IT general controls, application controls, cybersecurity controls, and controls that support financial reporting.
Working within the internal audit function, the IT Auditor scopes engagements, tests controls, documents findings, and recommends improvements. The role provides independent assurance to management and the audit committee that technology risk is being managed. It does not design or operate the controls it audits.
This is a hands-on assurance role for a professional who is comfortable with both technology and structured audit methodology.
Key responsibilities
Audit planning and scoping
- Support risk-based audit planning across the technology environment.
- Define audit scope, objectives, and test procedures.
- Identify key controls and risks for each engagement.
- Prepare audit programs and workpaper templates.
- Tailor coverage to [Company]'s environment: [cloud platforms, ERP, key applications, infrastructure].
IT general controls testing
Test IT general controls across access management, change management, and operations. Evaluate:
- Logical access, provisioning, and segregation of duties
- Change management and release controls
- Backup, job scheduling, and operations
- Configuration and security baseline controls
Application controls and SOX [if in scope]
Where SOX or a similar regime applies and the work is in [Company]'s audit plan, test application controls and the IT dependencies of financial reporting. Assess automated controls, interfaces, and key reports, and coordinate with financial audit teams on control reliance.
Cybersecurity and infrastructure
- Assess controls across networks, servers, databases, and cloud services.
- Evaluate vulnerability management and security monitoring.
- Test controls against the frameworks [Company] uses, such as [NIST CSF / ISO/IEC 27001].
Findings and reporting
Document exceptions clearly, quantify risk, and write actionable findings. Review results with control owners, who own and carry out remediation, agree action plans and dates, and prepare reporting for audit leadership.
Follow-up and continuous improvement
Track management's remediation of prior findings and test that fixes work before findings are closed. Support the adoption of data analytics and continuous auditing techniques.
Required qualifications
- Bachelor's degree in Information Systems, Accounting, Computer Science, or a related discipline, or equivalent relevant experience.
- 3 to 6 years of experience in IT audit, internal audit, or a related controls or assurance role.
- Working knowledge of IT general controls and application controls, and of SOX where the role supports it.
- Familiarity with audit methodology and workpaper documentation standards.
- Understanding of common technology environments, including cloud and enterprise applications.
- Strong analytical and written communication skills.
Preferred certifications
One or more of: CISA, CIA, CISSP, CPA, or equivalent audit or security certification.
Technical knowledge
IT general controls, application controls, SOX IT testing, access management, change management, cybersecurity control assessment, cloud and infrastructure controls, audit methodology, workpaper documentation, and data analytics for audit.
Success in the first year
- Assigned IT audits are completed to plan, with workpapers that pass review.
- [If SOX applies] ITGC testing is completed for in-scope systems on schedule.
- Findings are agreed with control owners, and remediation is tracked and verified before closure.
About [Company]
[Two or three sentences about your organization, the maturity of your program, and what the first year looks like. Candidates in this field respond to honesty about whether they are joining a build or an established function.]
Post this role on GRC Careers
Reach professionals who specialize in IT audit and controls testing rather than hoping they find you in a general feed. A person reviews every posting before it goes live, usually within one business day.
See how others are hiring
Review open GRC jobs to benchmark scope, level, and posted pay before you publish yours.
Stay close to the market
Job alerts
Get new GRC jobs sent to you as they post.
Newsletter
Hiring trends, salary signals, and new templates from GRC Careers.
Frequently asked questions
What does an IT Auditor do?
An IT Auditor evaluates whether technology controls are well designed and operating effectively. They test IT general controls, application controls, and cybersecurity controls, document findings, and give independent assurance that technology risk is being managed.
What qualifications and certifications does an IT Auditor need?
Most bring 3 to 6 years in IT audit or a related controls role, plus a bachelor's degree in information systems or accounting. The most common certification is CISA, and many also hold CIA, CISSP, or CPA.
What frameworks does an IT Auditor use?
Common references include COBIT for IT governance and controls, the NIST Cybersecurity Framework, ISO/IEC 27001, SOX requirements for IT general controls where the organization is subject to them, and the IIA's Global Internal Audit Standards.
What are IT general controls?
IT general controls, or ITGCs, are the foundational controls over access management, change management, and operations that support the reliability of applications and data. They are a core focus of IT and SOX audits.