
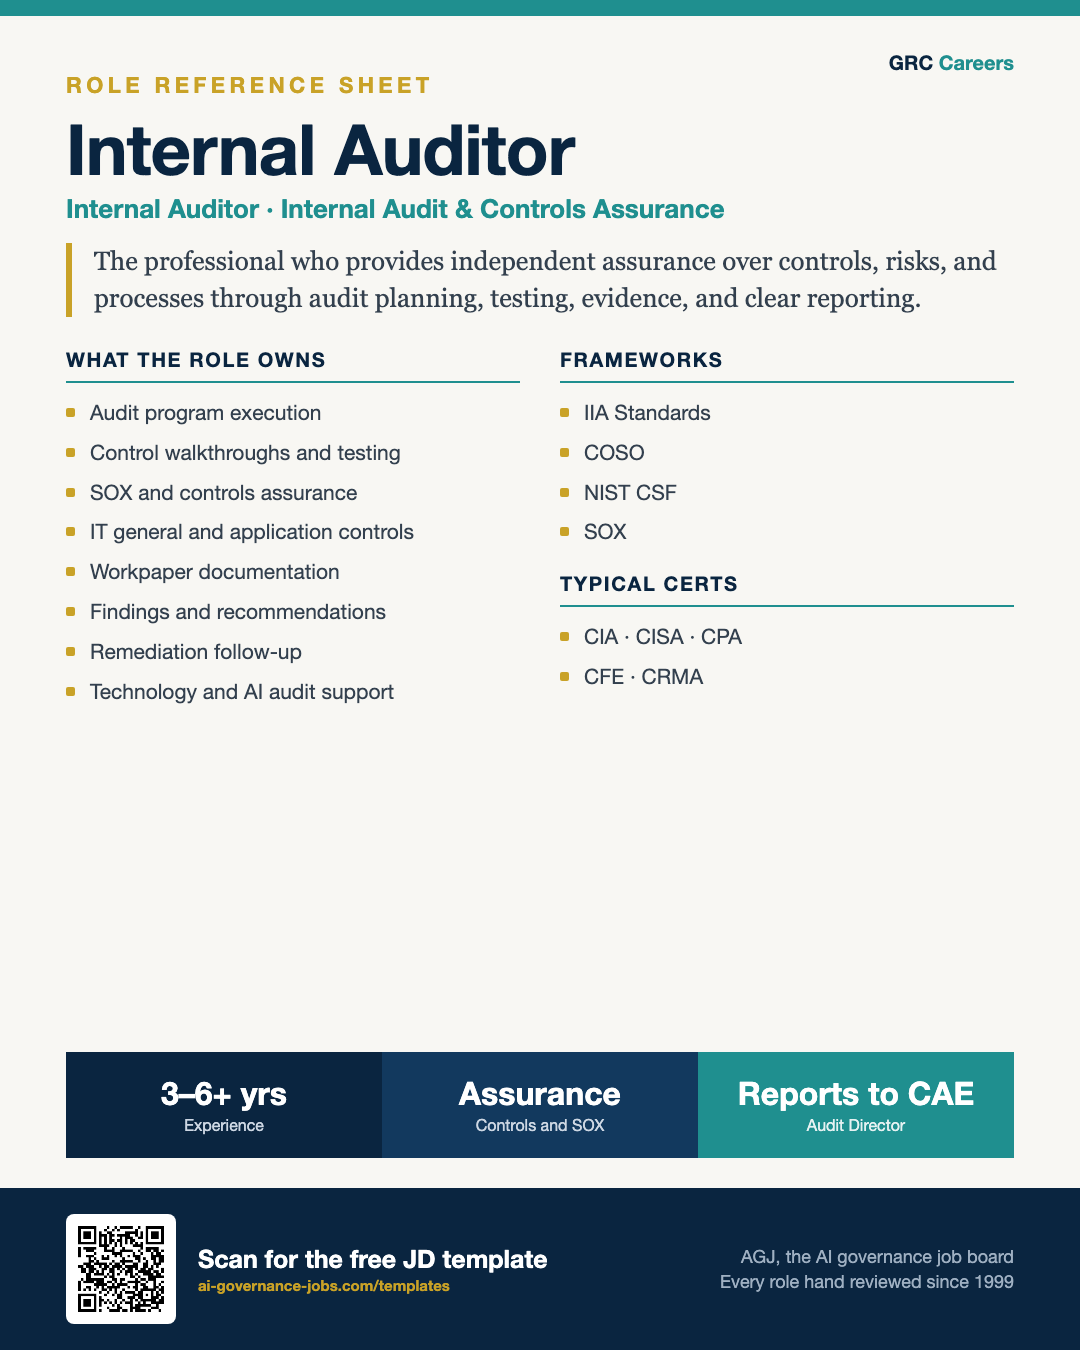
| Title | Internal Auditor |
|---|---|
| Department | Internal Audit |
| Reports to | [Internal Audit Manager / Director of Internal Audit / Chief Audit Executive] |
| Location | [Remote / Hybrid / On-site] |
| Employment type | Full-time |
| Experience | [3 to 6+] years |
| Salary | [Pay range, currency and pay period, plus any bonus and material benefits. Check the pay-disclosure rules for each location where you post.] |
Position overview
The Internal Auditor provides independent, objective assurance over [Company]'s governance, risk management, and control processes. The role plans and executes audits, tests controls, evaluates findings, and reports results that help management strengthen the control environment.
The Internal Auditor works across finance, operations, technology, and compliance to assess whether controls are designed and operating effectively, whether risks are managed, and whether processes meet policy and regulatory requirements. If [Company]'s audit plan covers AI and automated systems, the auditor also assesses the controls around them.
This role suits a disciplined, objective professional who is skilled in testing, documentation, and communicating findings with evidence and independence.
Key responsibilities
Audit planning
- Support risk-based audit planning and scoping.
- Develop audit programs, objectives, and test steps.
- Identify key risks and controls for each engagement.
- Coordinate timing and resources with stakeholders.
Fieldwork and testing
Execute audit fieldwork with rigor and independence:
- Perform walkthroughs and test control design and operation.
- Gather and document evidence in clear workpapers.
- Evaluate exceptions and determine root causes.
- Assess process, financial, operational, and technology controls.
Financial reporting and controls assurance [if in scope]
Where [Company] is subject to SOX or runs an internal control over financial reporting program, and that work is in this role's audit scope:
- Support SOX testing of internal control over financial reporting.
- Evaluate control gaps and deficiencies.
- Test IT general controls and application controls.
- Follow up on remediation of identified control issues and verify closure.
Findings and reporting
Document findings, risks, and recommendations clearly, discuss results with management, and prepare audit reports supported by evidence. Management owns the corrective action plans.
Technology and AI audits [if in scope]
Where [Company]'s audit plan includes them, support audits of technology, data, and AI or automated systems, assessing governance and controls against frameworks such as the NIST AI RMF.
Follow-up and standards
Track management's action plans, independently verify that agreed actions are complete before findings are closed, and perform work in conformance with the IIA's Global Internal Audit Standards.
Required qualifications
- Bachelor's degree in Accounting, Finance, Information Systems, Business, or a related field, or equivalent relevant experience.
- [Three to six] years of internal or external audit experience, set to the level you are hiring.
- Knowledge of the IIA's Global Internal Audit Standards, COSO, and internal control concepts.
- Experience with control testing, and with SOX or IT audit where the role requires it.
- Strong analytical, documentation, and workpaper skills.
- Ability to communicate findings clearly and maintain independence.
Preferred certifications
Preferred, depending on audit focus: CIA, CISA, CPA, CFE or CRMA.
Technical knowledge
Internal audit, risk-based audit planning, control design and operating effectiveness testing, SOX and internal control over financial reporting where in scope, IT general and application controls, data analytics, workpaper documentation, and audits of technology and AI systems where they are in the audit plan.
Success in the first year
- Assigned audits are completed to plan, with workpapers that pass review.
- Findings are supported by evidence, rated consistently and agreed with management.
- Management actions are tracked, and closure is verified before findings are closed.
- [If in scope] SOX testing cycles are completed on schedule.
About [Company]
[Two or three sentences about your organization, the maturity of your program, and what the first year looks like. Candidates in this field respond to honesty about whether they are joining a build or an established function.]
Post this role on GRC Careers
Reach professionals who specialize in internal audit and controls assurance rather than hoping they find you in a general feed. A person reviews every posting before it goes live, usually within one business day.
See how others are hiring
Review open GRC jobs to benchmark scope, level, and posted pay before you publish yours.
Stay close to the market
Job alerts
Get new GRC jobs sent to you as they post.
Newsletter
Hiring trends, salary signals, and new templates from GRC Careers.
Frequently asked questions
What does an Internal Auditor do?
An Internal Auditor provides independent assurance over an organization's controls, risks, and processes. They plan and execute audits, test controls, document evidence, and report findings and recommendations that help management strengthen the control environment.
What qualifications and certifications does an Internal Auditor need?
Most Internal Auditors have a bachelor's degree in accounting, finance, or information systems and 3 to 6 or more years of audit experience. Common certifications include the CIA, CISA, and CPA, plus CFE or CRMA depending on focus.
Who does an Internal Auditor report to?
An Internal Auditor typically reports to an Internal Audit Manager, a Director of Internal Audit, or the Chief Audit Executive, and internal audit generally maintains a reporting line to the Audit Committee.
What frameworks and standards does an Internal Auditor use?
Internal auditors work under the IIA's Global Internal Audit Standards and use COSO for internal control. Depending on the audit plan, they also reference the NIST Cybersecurity Framework, SOX requirements where the organization is subject to them, and controls over AI systems.