
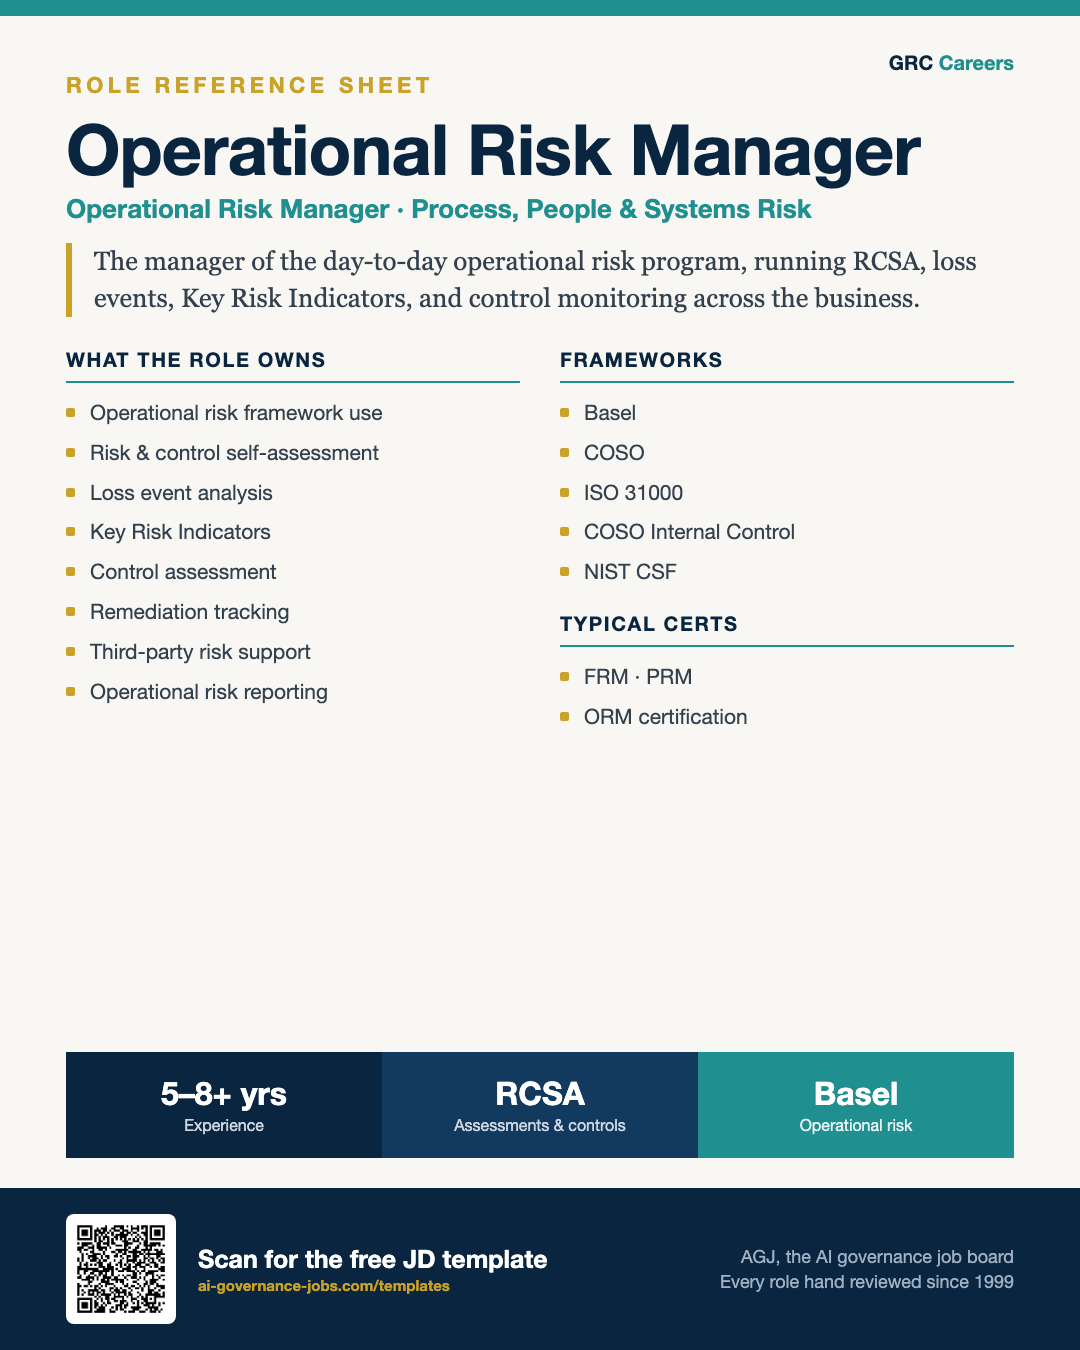
| Title | Operational Risk Manager |
|---|---|
| Department | Operational Risk / Enterprise Risk Management |
| Reports to | [Head of Operational Risk / Chief Risk Officer / VP of Risk] |
| Scope | [Second-line oversight role in the risk function / first-line risk role embedded in a business unit] |
| Location | [Remote / Hybrid / On-site] |
| Employment type | Full-time |
| Experience | [5 to 8+] years |
| Salary | [Pay range, currency and pay period, plus any bonus and material benefits. Check the pay-disclosure rules for each location where you post.] |
Position overview
The Operational Risk Manager runs [Company]'s operational risk program, applying the framework and methods that help the organization identify, assess, and manage risks arising from people, processes, systems, and external events.
The role partners with business units, compliance, technology, and internal audit to run risk and control self-assessments, track loss events, monitor Key Risk Indicators, and drive control improvements.
As operational and third-party dependencies grow more complex, the Operational Risk Manager helps the organization understand and reduce operational risk in line with COSO and, for banks and other firms that apply them, the Basel Committee's operational risk principles.
Choose the line of defense this role sits in. Business and control owners design, implement and operate their controls. In a second-line role, the Operational Risk Manager oversees, challenges and reports on those controls; in a first-line role, the manager helps the business design and run them.
Key responsibilities
Operational risk framework
- Apply and maintain the operational risk framework.
- Contribute to the operational risk appetite and tolerance statements that [the Chief Risk Officer / Board] approves.
- Align practices with COSO and, where they apply to [Company], the Basel operational risk principles.
- Maintain operational risk policies and procedures.
Risk and control self-assessment
Facilitate risk and control self-assessments (RCSA) across business units, including:
- Identification of key processes and risks
- Assessment of control design and effectiveness
- Rating of residual risk and gaps
- Agreement of remediation actions and owners
Loss events and incidents
- Capture and analyze operational loss events.
- Investigate root causes and control failures.
- Track remediation and lessons learned.
- Report loss trends to risk leadership.
Key Risk Indicators
Define, monitor, and report Key Risk Indicators (KRIs) for operational risk, escalating threshold breaches and emerging concerns to leadership.
Controls and remediation
Assess control effectiveness, identify gaps, and challenge business owners' remediation plans. Control owners design and implement the improvements; the Operational Risk Manager tracks them and confirms they work.
Third-party and resilience
- Support third-party and outsourcing risk assessment.
- Contribute to business continuity and resilience.
- Assess process and technology dependencies.
- Support scenario analysis for operational risk.
Reporting and analytics
Prepare operational risk reporting and analytics for leadership and risk committees, including dashboards, heat maps, and trend analysis.
Required qualifications
- Bachelor's degree in Risk Management, Finance, Business, or a related discipline, or equivalent experience.
- 5 to 8+ years of experience in operational risk, internal control, audit, or a related field.
- Experience facilitating RCSA and analyzing loss events.
- Working knowledge of operational risk frameworks and control concepts.
- Strong analytical and documentation skills.
- Experience with GRC tools and risk reporting preferred.
Preferred certifications
One or more of: FRM, PRM, or an operational risk management (ORM) certification.
Technical knowledge
Operational risk management, risk and control self-assessment, loss event analysis, Key Risk Indicators, control assessment, root cause analysis, third-party risk, business continuity, scenario analysis, and GRC platforms, aligned to COSO and, where applicable, Basel.
Essential competencies
Analytical rigor, attention to detail, stakeholder engagement, clear communication, problem solving, and the ability to influence control owners.
Success in the first year
- RCSAs are completed for [priority business units] on schedule.
- Loss events are captured and analyzed, with root causes recorded.
- Key Risk Indicators are defined for key risks, with thresholds and escalation routes.
- Remediation actions have owners and dates, and overdue items are escalated.
About [Company]
[Two or three sentences about your organization, the maturity of your program, and what the first year looks like. Candidates in this field respond to honesty about whether they are joining a build or an established function.]
Post this role on GRC Careers
Reach professionals who specialize in operational risk management rather than hoping they find you in a general feed. A person reviews every posting before it goes live, usually within one business day.
See how others are hiring
Review open GRC jobs to benchmark scope, level, and posted pay before you publish yours.
Stay close to the market
Job alerts
Get new GRC jobs sent to you as they post.
Newsletter
Hiring trends, salary signals, and new templates from GRC Careers.
Frequently asked questions
What does an Operational Risk Manager do?
The Operational Risk Manager runs the day-to-day operational risk program. They facilitate risk and control self-assessments, analyze loss events, monitor Key Risk Indicators, and work with the business to close control gaps.
What qualifications and certifications does an Operational Risk Manager need?
Most bring 5 to 8 or more years in operational risk, internal control, or audit. Helpful certifications include FRM, PRM, and operational risk management credentials, along with a degree in risk, finance, or business.
Who does an Operational Risk Manager report to?
The role typically reports to the Head of Operational Risk, the Chief Risk Officer, or a VP of Risk, and partners with business units, compliance, technology, and internal audit.
What frameworks does an Operational Risk Manager use?
Common reference points include COSO for internal control and enterprise risk, and ISO 31000. Banks and other firms supervised under Basel rules also apply the Basel Committee's operational risk principles. The NIST Cybersecurity Framework supports technology-related risk.