
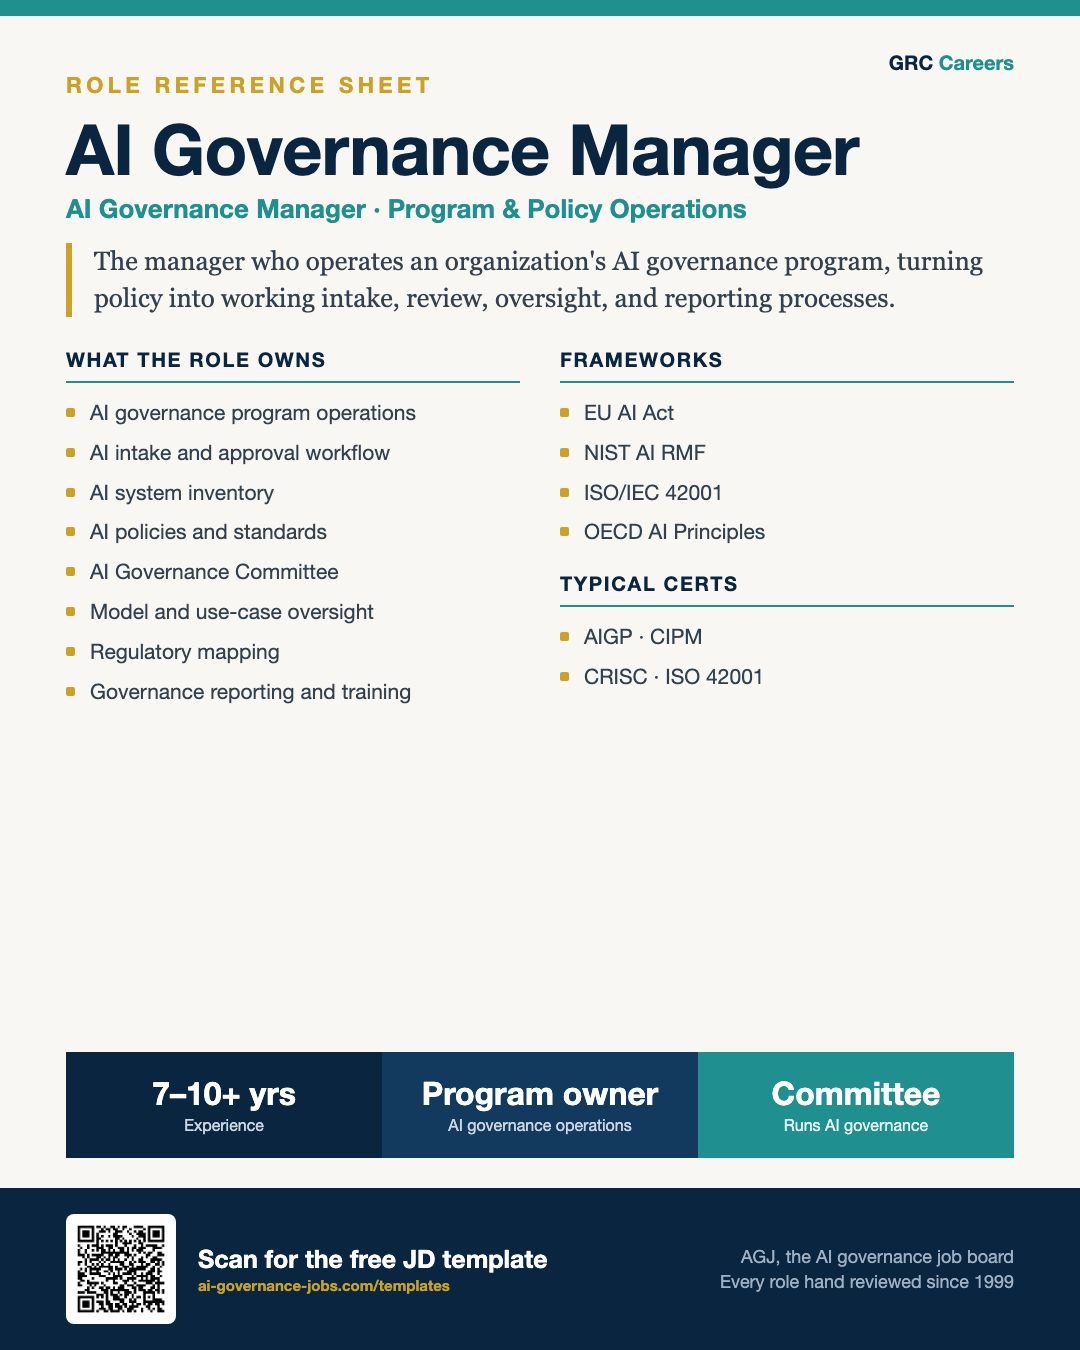
| Title | AI Governance Manager |
|---|---|
| Department | AI Governance / Risk & Compliance |
| Reports to | [Head of AI Governance / Chief Risk Officer / CISO] |
| Location | [Remote / Hybrid / On-site] |
| Employment type | Full-time |
| Experience | [7 to 10+] years |
| Salary | [Pay range, currency and pay period, plus any bonus and material benefits. Check the pay-disclosure rules for each location where you post.] |
Position overview
The AI Governance Manager leads the operation of [Company]'s AI governance program. This role turns AI policy and strategy into working processes, managing the intake, review and monitoring of AI systems across the organization. The manager operates the workflow; approval of AI use cases and acceptance of residual risk sit with [the AI Governance Committee / named executives], and the authority to pause or escalate a deployment rests with [describe who].
The AI Governance Manager coordinates across legal, compliance, privacy, security, data governance, and business teams so AI is developed and deployed responsibly and in line with the requirements that apply. Legal and compliance colleagues interpret which laws apply; the manager turns their conclusions into controls. The role also manages the AI system inventory, governance committee operations, and reporting.
As AI adoption scales, the AI Governance Manager is the connective tissue between policy and practice, making governance practical for the teams that build and use AI.
Key responsibilities
Governance program operations
- Run the AI intake and review workflow end to end, routing decisions to the people who hold approval authority.
- Record who approved each AI system, who accepted residual risk, and the conditions attached.
- Maintain the enterprise AI system inventory and risk classifications.
- Operate the AI Governance Committee, including agendas, materials, and decisions.
- Track governance metrics and program maturity over time.
Policy and standards
Develop, maintain, and socialize AI policies, standards, and procedures, covering:
- Responsible and ethical AI principles
- Model documentation and approval requirements
- Human oversight, transparency, and disclosure
- Acceptable use of generative AI and AI agents
Model and use-case oversight
- Coordinate risk reviews of AI use cases and models before deployment.
- Ensure documentation, testing, and monitoring requirements are met.
- Partner with model owners on control implementation and remediation.
- Confirm that system owners run the monitoring the policy requires for drift, performance and incidents, and escalate gaps.
Laws, regulations and voluntary frameworks
Track the AI laws and regulations that apply to [Company], such as the EU AI Act and [applicable state, sector or national rules], and map their requirements to internal controls with Legal and Compliance. Separately, align the program with the voluntary frameworks and standards the organization adopts, such as the NIST AI Risk Management Framework and ISO/IEC 42001.
Third-party AI governance
- Coordinate governance reviews of AI vendors and tools.
- Support due diligence and contractual AI provisions.
- Maintain oversight of externally sourced models and services.
Reporting and enablement
- Produce governance reporting for leadership and committees.
- Deliver training and guidance to teams building and using AI.
- Maintain governance documentation and evidence for audits.
- Drive continuous improvement of the governance program.
Required qualifications
- Bachelor's degree in Information Systems, Computer Science, Data Science, Law, Business, or a related discipline, or equivalent experience.
- [7 to 10+] years of experience in governance, risk, compliance, privacy, or technology program management, including AI or data governance.
- Experience operating governance committees, policies, or control programs.
- Working knowledge of AI and machine learning concepts and lifecycle.
- Strong program management, facilitation, and cross-functional communication skills.
Preferred certifications
One or more of: AIGP, CIPP, CIPM, CRISC, CISM, ISO/IEC 42001 Lead Implementer.
Technical knowledge
AI governance program management, responsible AI, AI policy and standards, model lifecycle oversight, AI risk classification, regulatory mapping, third-party AI risk, data governance, and GRC and governance platforms.
Essential competencies
Program management, cross-functional facilitation, stakeholder influence, clear written communication, pragmatic problem solving, and translating policy into operational process.
Success in the first year
- [If building the program] Stand up a working AI intake and review workflow with defined approval routes.
- [If building the program] Complete a first enterprise AI system inventory with risk classifications.
- [If the program is established] Keep the inventory current and shorten the time from intake to decision.
- Run the AI Governance Committee on a regular cadence, with recorded decisions and action owners.
- Map the applicable AI regulations to internal controls, with Legal and Compliance review.
- Establish governance reporting for leadership.
- Deliver AI governance training to priority teams.
About [Company]
[Two or three sentences about your organization, the maturity of your program, and what the first year looks like. Candidates in this field respond to honesty about whether they are joining a build or an established function.]
Post this role on GRC Careers
Reach professionals who specialize in AI governance and program management rather than hoping they find you in a general feed. A person reviews every posting before it goes live, usually within one business day.
See how others are hiring
Review open AI governance jobs to benchmark scope, level, and posted pay before you publish yours.
Stay close to the market
Job alerts
Get new AI governance jobs sent to you as they post.
Newsletter
Hiring trends, salary signals, and new templates from GRC Careers.
Frequently asked questions
What does an AI Governance Manager do?
An AI Governance Manager operates an organization's AI governance program day to day. They run AI intake and approval workflows, maintain the AI system inventory, coordinate risk reviews, and keep policies, reporting, and the AI Governance Committee running.
What qualifications and certifications does an AI Governance Manager need?
Most AI Governance Managers bring 7 to 10 or more years in governance, risk, compliance, privacy, or technology program management, including AI or data governance. Common certifications include AIGP, CIPP, CIPM, and ISO/IEC 42001 Lead Implementer.
Who does an AI Governance Manager report to?
The role commonly reports to a Chief AI Officer, Head of AI Governance, Chief Risk Officer, or Chief Compliance Officer, and typically coordinates or supports the AI Governance Committee.
What frameworks does an AI Governance Manager use?
They separate laws from voluntary frameworks. The EU AI Act is a law that applies to organizations within its scope; the NIST AI Risk Management Framework and the OECD AI Principles are voluntary; ISO/IEC 42001 is an international management-system standard an organization can certify against. Legal and compliance colleagues decide which laws apply, and the manager maps them to internal policies and controls.